

Can We Trust AI to Act?
As AI moves from generating answers to taking actions, this interview examines the data architecture, identity, governance, security and human accountability required to scale agentic AI responsibly.
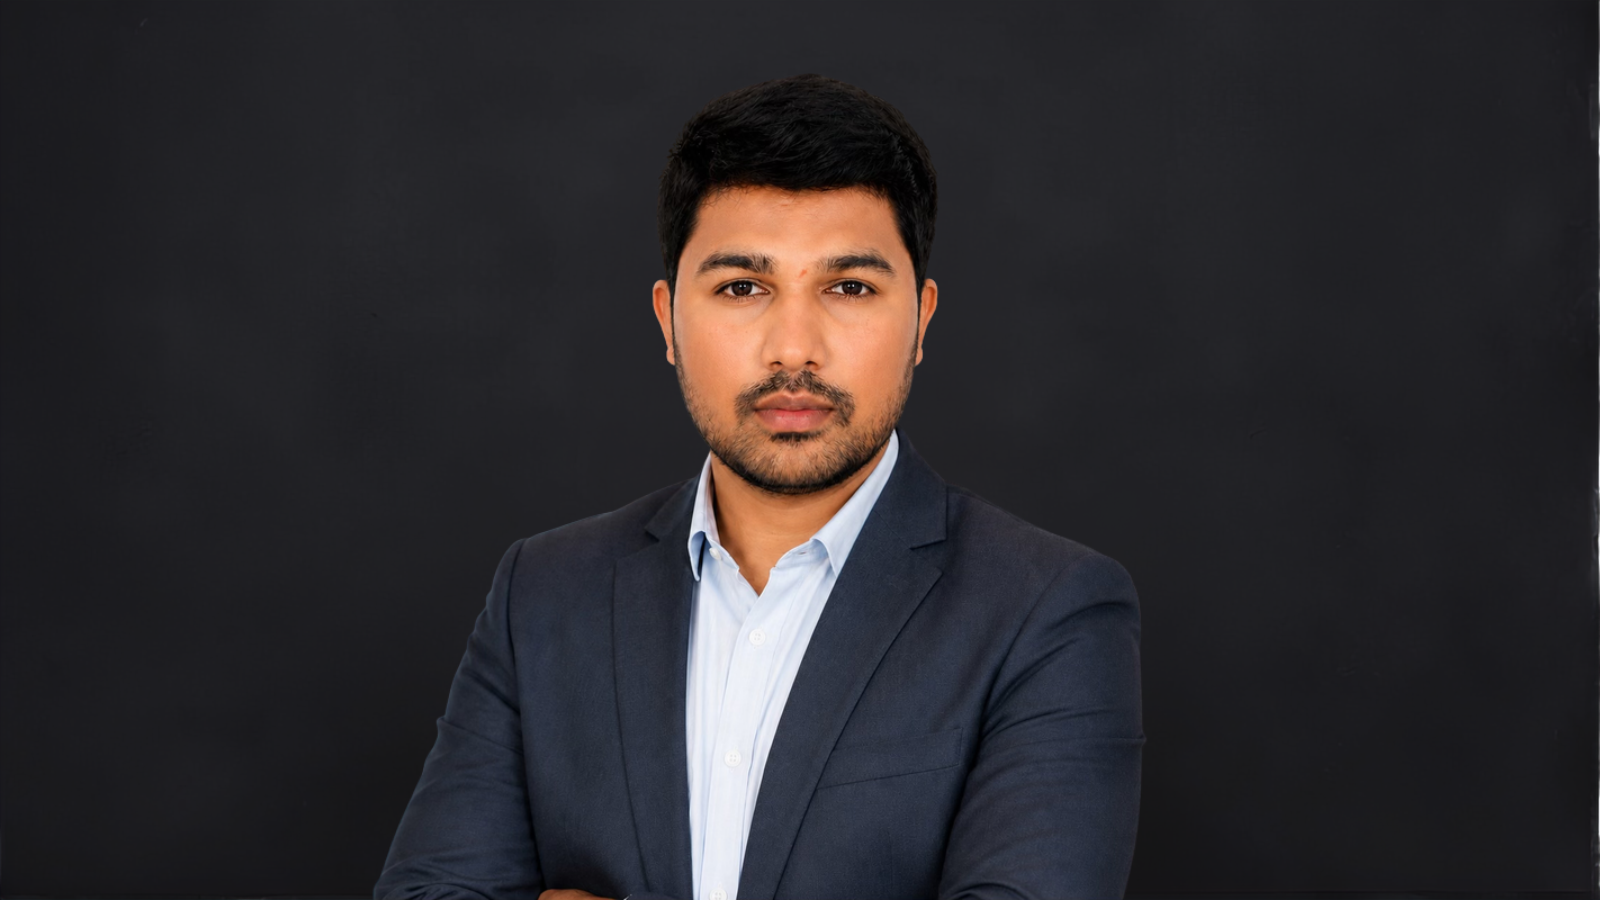
Gopichand Mannava
Chief Data Architect | Enterprise Data & AI Leader
State of Connecticut
Power Questions
Min Read
Domains Covered
Published
Gopichand Mannava, M.Eng.., MBA, PMP is Chief Data & AI Architect for the State of Connecticut and an independent researcher focused on trusted agentic AI, enterprise data architecture, AI governance, cybersecurity, digital identity, and public-sector decision intelligence. He works with executive stakeholders across finance, human resources, technology, analytics, and governance to strengthen the data and operating foundations that support secure, accountable, and scalable public services.
His work connects enterprise modernisation with responsible AI adoption, helping complex organisations design systems in which data quality, identity-aware access, security, human oversight, and measurable outcomes are addressed together. His research examines how public institutions can use AI to improve decision-making and service delivery while protecting privacy, transparency, accountability, and public trust.
Mannava contributes to the field through published thought leadership, executive and advisory board service, judging, peer review, and technology-community leadership. He has been recognised as a 2026 Oracle Analytics and AI Leader Worldwide and an AI150 Award recipient at MachineCon USA 2026. He serves as a Claro Awards judge and a peer reviewer for the Women in Machine Learning Workshop at NeurIPS 2026.
This interview explores what it takes to build Trusted Agentic AI, from critical data architecture and identity-aware access to governed actions, continuous oversight and graduated autonomy. It also examines how public-sector organisations can move beyond isolated AI pilots whilst maintaining accountability, transparency, security and public trust.
As a Chief Data & AI Architect working in a complex public-sector environment, what does a “critical data architecture” mean today, and why is it essential before organisations scale agentic AI?
Critical data architecture is the enterprise foundation that determines whether artificial intelligence becomes dependable decision intelligence or remains a collection of disconnected experiments. It is “critical” because it connects data, people, processes, systems, security, governance, and mission outcomes in a way that allows an organization to operate responsibly at scale.
Before an organization gives AI agents access to enterprise information or workflows, it needs more than a capable model. It needs clear data ownership, authoritative source systems, interoperability, quality controls, metadata, lineage, provenance, identity-aware access, security-by-design, and audit records. Otherwise, an agent may produce a plausible answer without anyone being able to establish whether its information was current, authorized, complete, or reliable.
In public-sector settings, that distinction matters even more. Decisions can affect public services, privacy, eligibility, finances, safety, and trust. The leadership question is not simply, “Can an agent complete this task?” It is, “Can we explain what information it used, who had authority to access that information, what it was permitted to do, and who is accountable for the outcome?”
That is why data architecture is no longer only a technical discipline. It is a leadership capability that enables responsible innovation. When data, governance, identity, and security are designed together, organizations can move faster with AI while protecting the people and missions they serve.
What makes agentic AI fundamentally different from traditional automation and earlier generations of generative AI?
Traditional automation generally follows predefined rules: if a defined event occurs, a system performs a defined action. Generative AI added the ability to draft, summarize, translate, classify, and create content. Agentic AI goes further. It can interpret an objective, plan multiple steps, retrieve information, invoke approved tools, and recommend or perform actions across a workflow.
That added capability creates a different risk profile. An agent may interact with sensitive data, use multiple systems, take actions that affect records or processes, and adapt its path based on changing context. The issue is therefore not only whether its output is accurate. Leaders must understand the boundaries of its authority, the tools it can use, the data it can see, the decisions it can influence, and the controls that prevent unintended consequences.
Organizations should treat agentic AI as an enterprise architecture and accountability challenge, not merely an AI-tool selection exercise. The most successful deployments will make the connection between purpose, authority, data, identity, security, monitoring, and human responsibility explicit from the beginning.
The practical implication is simple: do not give an agent more access, authority, or autonomy than the organization can govern, monitor, explain, and, when necessary, stop.
You describe a “Trusted Agentic AI” model. What are the essential governance and security components of that model?
I use a practical four-part model: Trusted Data, Trusted Identity, Trusted Action, and Trusted Oversight. It is designed to help leaders translate broad principles of responsible AI into operational design choices.
Trusted Data means an agent is grounded in governed, authoritative, current, quality-controlled information with clear provenance. Organizations should know which sources are approved, what the data means, how current it is, what limitations apply, and how sensitive information is protected. A powerful model cannot compensate for unreliable or poorly governed data.
Trusted Identity means every human, agent, application, and service has a defined identity and receives only the access appropriate to its role, purpose, and sensitivity. Identity is the control plane for trustworthy AI. It makes it possible to know who initiated an action, which agent performed it, what permissions were used, and whether access remained within approved boundaries.
Trusted Action means leaders define what an agent may retrieve, recommend, draft, prepare, or execute. This should include action thresholds, approval requirements, tool-use restrictions, segregation of duties, and controls for high-impact decisions. An AI agent should not move from recommendation to execution simply because it can.
Trusted Oversight means maintaining logs, monitoring, testing, evaluation, escalation paths, rollback mechanisms, periodic review, and named accountable owners. Oversight must continue after launch because agents can encounter new data, new tools, new contexts, and new failure modes over time.
Together, these four elements make trust a design requirement rather than a promise. The model complements established responsible-AI practices such as governance, data management, performance evaluation, and continuous monitoring.
How can organisations create meaningful human accountability when AI agents operate across workflows and systems?
Human-in-the-loop cannot mean a person simply clicks “approve” after an agent has completed a complex chain of actions. Meaningful accountability begins before deployment, when the organization decides where humans must exercise judgment, who has authority to intervene, how exceptions are escalated, and how errors can be corrected or reversed.
A useful approach is graduated autonomy. Assistive agents can retrieve, summarize, draft, and recommend but cannot alter records or initiate consequential actions. Supervised agents can prepare or stage an action, but a designated person validates and authorizes the final step. Controlled execution may be appropriate only for narrow, low-risk, reversible tasks with strict permissions, continuous monitoring, and clear stop-and-rollback procedures.
The right level of autonomy depends on the potential consequence of error. Where an outcome affects a person’s rights, benefits, privacy, finances, safety, or access to services, human accountability must remain explicit and meaningful. Leaders should also define the responsibility chain: the business owner accountable for outcomes, the technical owner responsible for reliability and controls, the data owner responsible for source quality, and the risk, legal, privacy, and security functions responsible for appropriate guardrails.
Responsible AI does not remove people from important decisions. It equips people with better information while preserving the authority and accountability required to make high-impact decisions responsibly.
What will distinguish public-sector organisations that scale agentic AI responsibly from those that remain in pilot mode or create new risks?
By 2030, the leaders will not necessarily be the organizations that purchased the most advanced model. They will be the organizations that built the strongest institutional capability around trustworthy AI.
That capability includes governed and interoperable data, clear business ownership, modern digital identity, resilient cybersecurity, reusable risk assessment, workforce readiness, procurement standards, lifecycle monitoring, and outcome measures that go beyond productivity. Public-sector leaders should ask whether AI improves service quality, decision reliability, accessibility, resilience, transparency, equity, and public trust, not merely whether it automates more tasks.
Organizations that remain stuck in pilot mode often treat AI as a series of isolated experiments. They can create compelling demonstrations, but they cannot move safely into production because the data foundations, operating model, accountability structures, and controls are not ready. Organizations that create new risks often make the opposite mistake: they scale quickly without clear ownership, system boundaries, or oversight.
The strategic opportunity is not merely to automate individual tasks. It is to build accountable decision intelligence: an enduring operating capability in which people, data, processes, and AI work together to improve outcomes while protecting the public interest.
More Visionary Spotlights
Want to be featured in a Visionary Spotlight?
We interview C-suite leaders shaping the future of data, AI and analytics. If that's you, or someone you know, get in touch.